


Cloud security and visibility with Sysdig and Sumo Logic
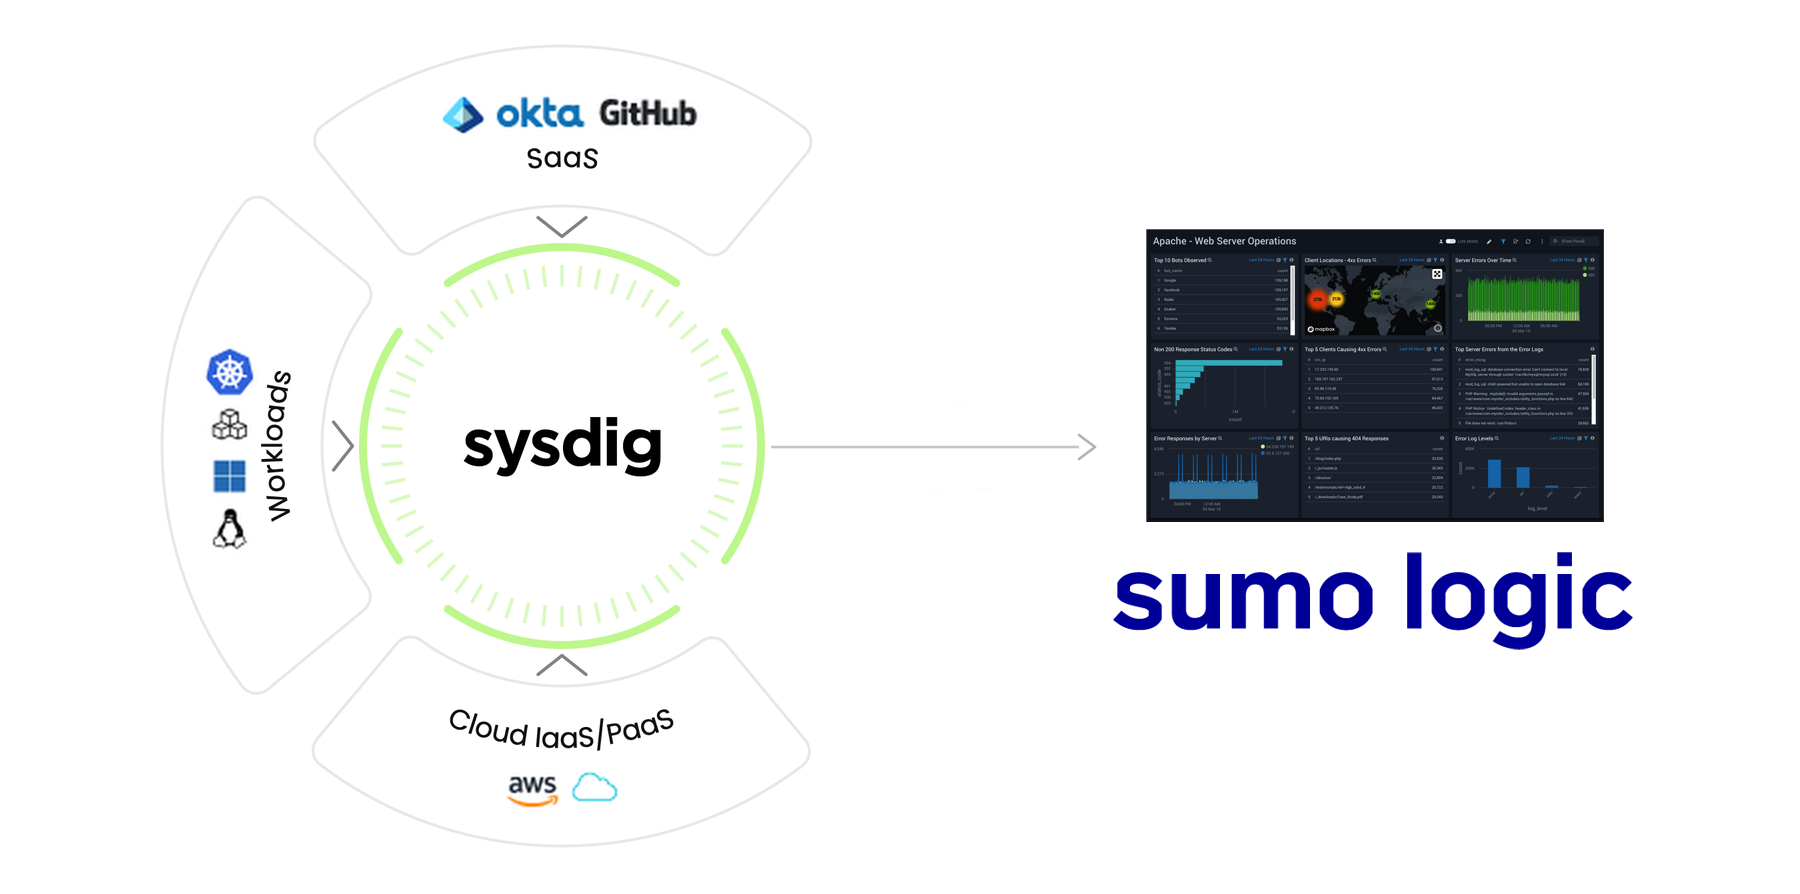
Sumo Logic triages alerts and detect threats across all your data sources to speed up incident investigations in your security operations center (SOC). Sysdig delivers threat insights from containers, hosts, Kubernetes, and clouds into Sumo Logic to enable correlation of findings and in-depth analysis with data from other sources in your environment.
By integrating the capabilities of SIEM and security analytics, with a cloud-native application protection platform (CNAPP), Sumo Logic and Sysdig give you the insights you need to protect, investigate, and respond to complex cloud threats.
Customer value
- Move from detection to action faster by bringing Sysdig’s runtime threat visibility and context into Sumo Logic’s cloud SIEM workflows.
- Improve risk prioritization with richer vulnerability context—including CVE details, severity, affected resources, asset metadata, cloud provider, and workload information.
- Reduce alert and data noise by using targeted, deduplicated findings instead of repeatedly ingesting large vulnerability snapshots.
- Lower operational costs by limiting data processing to relevant or newly identified findings rather than millions of duplicated records.
- Streamline vulnerability operations by enabling workflows such as grouping findings by cloud provider and creating actionable remediation tickets.
- Unify security context in the existing SIEM so analysts can correlate Sysdig runtime findings with broader security telemetry without constantly switching tools.
- Extend the value of existing investments by connecting specialized cloud-runtime security intelligence with Sumo Logic’s SIEM and analytics capabilities.
Learn more
To get started with Sysdig and Sumo Logic, check out our documentation.
SIEM/SOAR